


Medical Intelligence Recording AssistantMedMentis
Draft reports from the doctor-patient conversation. In development.
See the solution
From Frankfurt, certified to ISO/IEC 27001.
Sector and size decide whether NIS 2 applies to you (Section 28 BSIG). Result right away, no personal details.
All about GRC & ComplianceTell us about your situation. We will get back to you personally.
Request an initial call15 minutes, free, no obligation.
Prefer to write: go to the contact pageCybersecurity, GRC & compliance and AI solutions from one partner, based in Frankfurt am Main. Our services →
Ask your question by voice, our AI answers right away.
One click starts the conversation with our AI. We do not keep any recordings. Privacy
Designed to listen and draft the medical report, typically in under 60 seconds. In development, pilot program for hospitals.In development, pilot for hospitals.
This is how the GAD Defense Engine brings test runs, attack paths, findings and measures together in one place, so IT and management work from the same basis. The view uses sample data, the test runs come from RedMentis today.
If this measure closes the path, the next run confirms it.
Each finding appears with its attack path, not in a loose list.
After each measure, the next run checks whether the path is closed.
Concept view with sample data
Request a RedMentis demoOur three core services work together to make organizations more resilient in technology, regulation, and organization.
For organizations that want to continuously improve their security posture, detect attacks early, and make technical risk understandable and manageable.
For companies that want to meet regulatory requirements in a structured way, document security measures, and ground management decisions in solid evidence.
For companies that want to put AI to work productively without losing control over data, permissions, results, and regulatory requirements.

Regulation, AI adoption, and cyber risk push companies to build security they can prove and manage.
We check and protect your devices, email, website and accounts. Choose the package that fits your company and expand when you need to.
15 minutes by phone
 First call
Free
No preparation, no cost
Request a first callSecurity essentials
Go€190€129
one-off, plus VATper month, min. 3 months, plus VAT
Book packageBook packageGet free adviceEnhanced protection
Profrom €990from €890
one-off, plus VATper month, plus VAT
Book packageBook packageGet free adviceAdvanced protection
Enterprisefrom €1,490from €1,290
one-off, plus VATper month, plus VAT
Book packageBook packageGet free adviceAll prices net plus VAT, for businesses only.
Pick the question that best describes your situation. The link takes you straight to the matching service.
Draft reports from the doctor-patient conversation. In development.
See the solutionFinds attack paths and ranks measures by risk. In pilot operation.
See RedMentisOrders, stock, purchasing and invoices in one system.
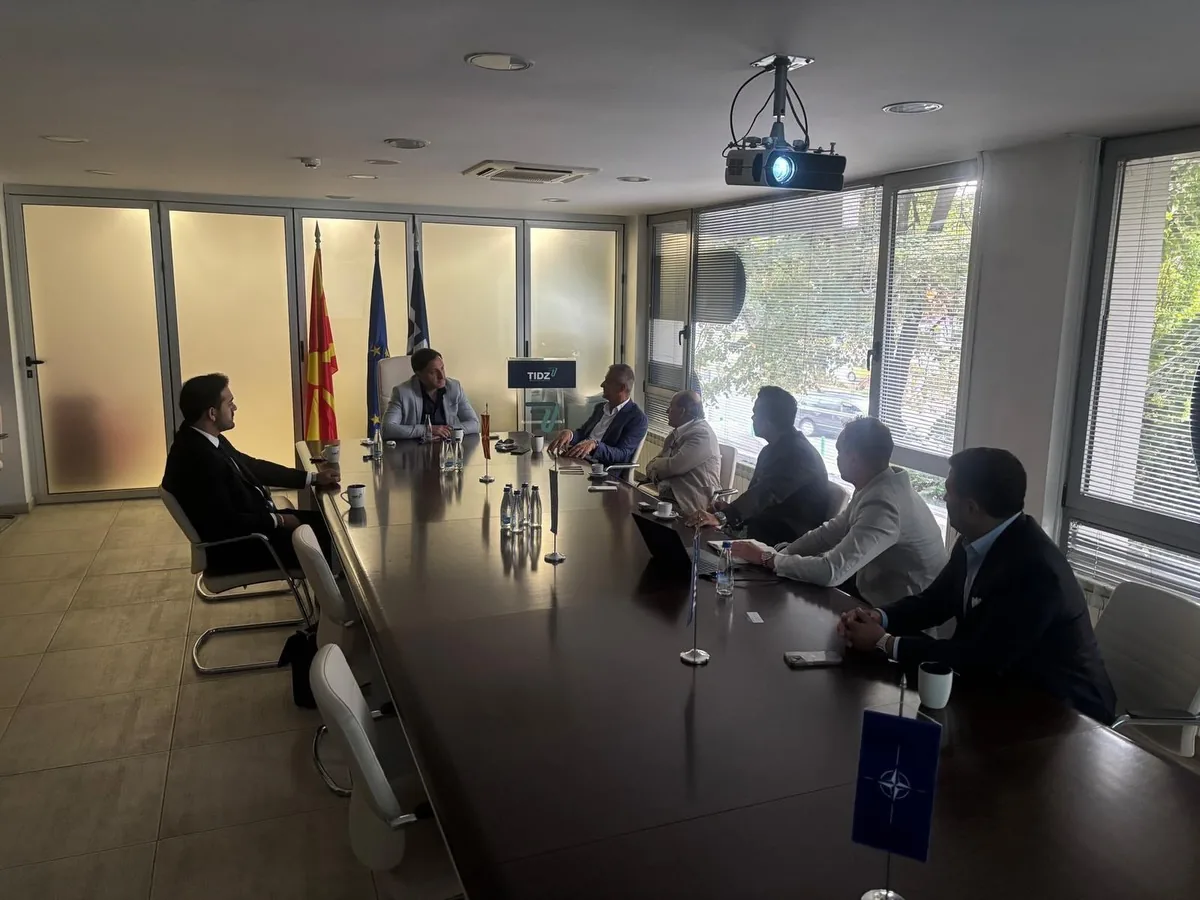
See StockMentisOur co-founder and CEO Abdussamed Nazik was part of a delegation to a European Ministry of Digital Transformation. Talks with the Minister and the national investment agency focused on AI and secure digital infrastructure.
germanaidefense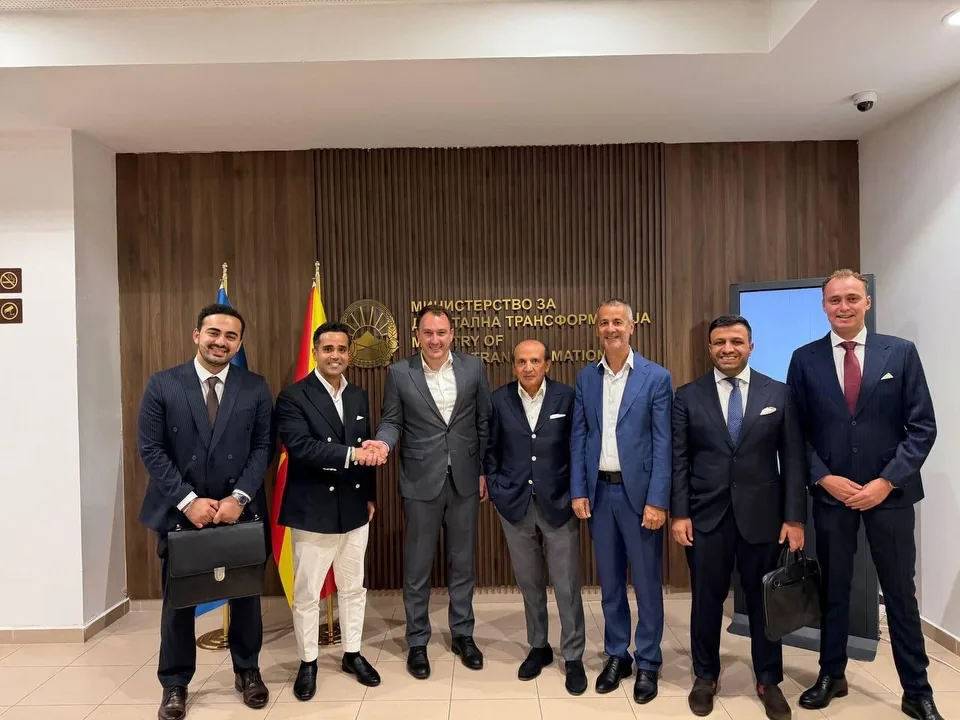
germanaidefense North Macedonia | Strategic Dialogue on AI and Digital Infrastructure
Our CEO @abdussamednazik was part of a delegation to North Macedonia. Topic: an AI Innovation Park for AI, energy and secure digital infrastructure.
GermanAI Defense GmbH
Short videos on everyday attacks, data centers and our work
Defense needs a system. Our software at the top, our services in the middle, the foundation of data centers and training at the base. Select a building block to see what it connects to.
Tap a building block
SOC monitoring around the clock, for data centers too, while RedMentis keeps testing between two pentests
More on CybersecurityDaily IT-security headlines, automatically curated. Tap any item to read the full report at the source.
Loading latest reports…
Headlines and short excerpts belong to their respective source and link there. No liability for third-party content.
We protect, manage, and improve the security posture of enterprises, industry, and critical infrastructure through three interlocking services: Cybersecurity (round-the-clock SOC monitoring for managed environments), GRC & Compliance (GDPR, NIS 2, EU AI Act), and AI Solutions (secure AI integration, LLM, and AI test automation). They are complemented by our software solutions Medical Intelligence Recording Assistant (draft medical reports from the conversation, in development), RedMentis (AI-driven attack path analysis, in pilot operation) and StockMentis (multichannel inventory management) plus two layers: data center and infrastructure projects that certified partners deliver under their own contracts while we manage and protect them, and the GAD Academy for training and enablement. Made in Germany, operated on your premises or in Germany.
Yes. We are based in Frankfurt am Main. From here we advise companies and organisations in Frankfurt and the Rhine-Main region on IT security: from penetration testing (a commissioned, controlled attack attempt on your systems) and preparing for NIS 2 (the EU directive with IT security obligations) to round-the-clock SOC monitoring. The Cybersecurity page gives an overview. Where mid-sized companies should start is covered in our article IT security consulting for mid-sized companies.
Governments, authorities and companies come to us with their requirements. We take on the project, structure it and lead the talks with everyone involved, from the authority to the grid operator. Design and construction are handled by certified partners with references in Germany, under their own contracts with you: German engineering, designed to Tier III criteria, with redundant power and cooling. We select the partners and manage the project. What gets built, we protect: access, network and round-the-clock SOC monitoring, with service and response times as agreed in the contract. The data location is set by contract.
The SOC (Security Operations Center, a control room for IT security) combines central event analysis on common SIEM platforms with AI-assisted anomaly detection. A SIEM gathers the security alerts from your entire network in one place. New events are pre-assessed automatically, critical cases follow fixed escalation levels. The AI filters the noise, people decide in the critical moment. SOC monitoring around the clock, service and response times as agreed in the contract.
RedMentis is our approach to AI-orchestrated security validation that complements the pentest: an AI that repeatably simulates attacker behavior, systematically scans applications, networks, and configurations for vulnerabilities, and reports findings with concrete reproduction steps, instead of just once a year like a classic pentest. Today we use RedMentis in pilot operation with selected customers, as a service delivered by GAD.
AI for your business processes: LLM integration into your existing systems, custom models for industry-specific tasks, and automation of document and data workflows. Designed for GDPR-compliant operation, on your premises or in a data center in Germany.
We validate ML models, LLMs, and data pipelines automatically across the entire lifecycle, from initial training to production. This includes drift detection, LLM hallucination tests, bias audits, and robustness checks against adversarial inputs (deliberately manipulated inputs). So after every test run you can see where your AI answers incorrectly, and you repeat the check regularly in production.
We define where your data is stored in the project and document it in the data processing agreement. Our default: data and processing in German data centers or on your premises, without cloud providers outside the EU if you prefer. If you already use a SIEM platform, we integrate them and explain what that means for data transfers to third countries. We are ISO/IEC 27001:2022 certified. Our architecture is designed for GDPR- and NIS 2-compliant operation and supports KRITIS evidence as well as the requirements of the EU AI Act.
We start with a free 15-minute first call to understand your situation and what you need. Within 2 to 4 weeks, we deliver a concrete proposal with an architecture outline and timeline. First productive steps (e.g., SOC onboarding or a RedMentis initial scan) often go live within 4 to 6 weeks. Both figures are guide values as of October 2026.